
Crypto & Bitcoin applications
Wallets, custody flows, on-chain integrations and exchange connectivity with key handling done correctly.
Some products can't be learned on. Payments, custody, trading, health records and anything handling other people's money need engineers who have shipped it before — and who design for the failure case first.
In fintech, crypto and high-traffic products, a slow endpoint or a security gap means lost funds, lost trust and lost customers.
Talk to our expertsWeak auth, exposed keys or unaudited code waiting to be found.
Systems that slow down or fail exactly when traffic peaks.
Payment, exchange and partner APIs that break in silent, costly ways.
High-security, high-performance systems — crypto and fintech workflows, complex APIs, hardened backends and deep performance work.
Wallets, custody flows, on-chain integrations and exchange connectivity with key handling done correctly.
Payments, ledgers, reconciliation, KYC/AML flows and reporting built to survive an audit.
Threat-modelled architecture, encryption at rest and in transit, secrets management and least-privilege access.
Versioned public APIs, webhooks, rate limiting, idempotency and documentation partners can build against.
Profiling, query tuning, caching layers and architecture changes that turn seconds into milliseconds.
Streaming data, websockets, order flow and event pipelines that hold up under bursty load.
Load testing, autoscaling, failover, observability and incident runbooks before you need them.
Independent review of an existing system with a prioritized remediation plan and fix support.
What comes in on the left, what goes out on the right — and what we build in the middle, connected to the tools your team already uses.
Map your workflow with usHardened backend
Secure, fast and audited
From first call to production — you see progress every week and know what comes next.
What can go wrong, what it costs, and what traffic and failure modes the system must absorb.
Data flows, trust boundaries, key management and the blast radius of every component.
Critical paths covered by automated tests and property checks before features stack on top.
Penetration-style review, dependency scanning, load testing and a remediation pass.
Metrics, alerts, tracing and documented incident response handed to your team at launch.
If you recognise yourself here, the first call will be a short one — we already know the questions to ask.
Products holding funds or moving money, where security is the product, not a feature.
Teams whose differentiation is engineering depth — latency, scale or algorithmic quality.
Live systems that are slow, fragile or failing under growth and need senior intervention.
Health, legal and finance operations with compliance and auditability requirements.
Fintech / crypto · USA
A secure Bitcoin/crypto wallet with real-time trading, biometric auth and hardware-grade key handling.
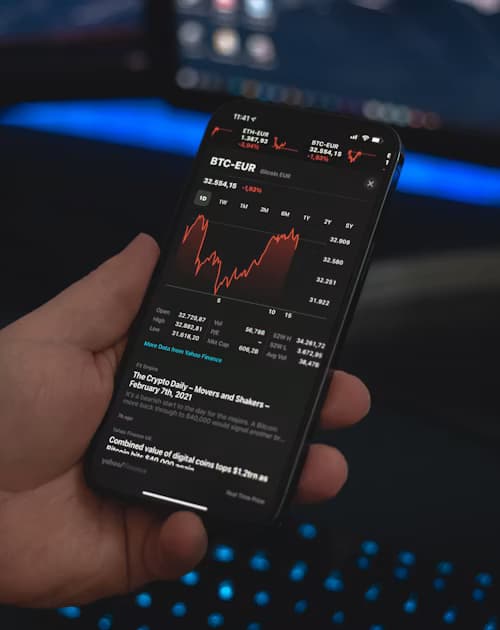
Start small and prove it, or go straight to the build. Fixed scope, clear deliverables.
One-time · 1–2 weeks
An independent read of your system with risks ranked by likelihood and blast radius.
Project · 12+ weeks
Senior-only engineering of the high-stakes core, with testing and hardening built into the price.
Fixed price · 2–4 weeks
A focused intervention on a slow or unstable production system, with measured results.
Quick answers about Critical Product Engineering. Don't see yours? Ask us directly.
Ask a questionYes. NDAs, background-checked engineers, VPN or VDI access, dedicated devices and working inside your cloud accounts are all normal for these engagements.
No, and we'd distrust anyone who said otherwise. We build to pass one and remediate findings, but the independent audit should stay independent. We'll recommend firms we've worked alongside.
Usually. Most performance problems are a handful of queries, a missing cache layer or a bad hot path — not the architecture. The Performance Rescue package finds out in two weeks, and a rewrite recommendation comes with evidence.
HSMs or managed KMS for key material, no secrets in code or CI logs, least-privilege IAM, and rotation policies documented at handover. For custody work, multi-sig and threshold schemes are designed in from the start.
Book a discovery call or get an MVP blueprint. No pressure, no jargon — just a clear plan for your idea, workflow or product.
Prefer email? hello@nexalinx.com